For years, business owners have heard the same advice: turn on multi-factor authentication (MFA), the extra code or phone prompt at login, and you’ve closed the biggest door. That advice is still right. But last week’s attack on Microsoft 365 customers is a reminder that people aren’t the only ones who sign in to your systems. Connected apps do too, and Microsoft 365 third-party app access is one of the easiest doors to overlook.
What happened
On October 15, an attacker used a stolen credential belonging to ConnectWise Cloud Backup (formerly SkyKick), a widely used service that backs up Microsoft 365 email and files, to sign in to customers’ Microsoft 365 environments. Security firm Huntress confirmed unauthorized sign-ins in more than 160 organizations within about a day, and Microsoft described it as an active supply-chain attack. ConnectWise shut the service down while it investigates. As of October 18, it said scheduled backups weren’t running and restores were unavailable. BleepingComputer has a clear summary of the timeline.
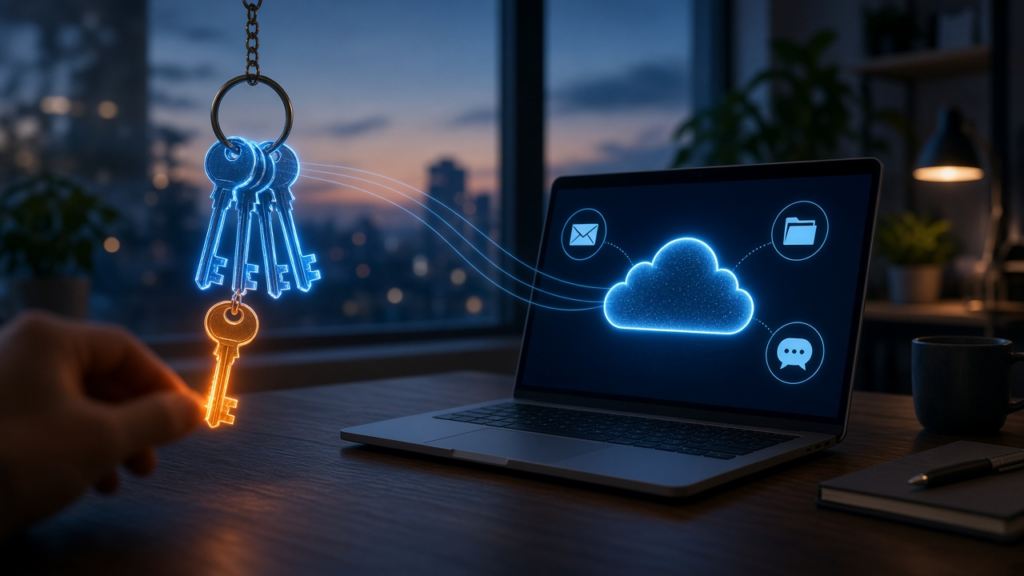
Here’s the part that matters for every business, whether or not you’ve ever heard of this vendor: MFA never came into play. The attacker didn’t log in as a person. They logged in as the app, using the app’s own secret key, and inherited every permission the business had already granted it. For a backup tool, that’s a lot: the ability to read and change email and attachments, OneDrive and SharePoint files, and Teams chats. In some cases, investigators saw connected apps give themselves administrator rights and plant new credentials so the attacker could come back later.
One administrator reported getting an alert that the app had promoted itself to email administrator in their account, even though they hadn’t used it in years.
Why this is a business issue, not just an IT one
Every time someone at your company clicks “Accept” to connect a tool to Microsoft 365, whether it’s a scheduling app, an e-signature service, a CRM plug-in, or a backup product, they’re handing that vendor a key. That consent doesn’t lapse on its own: the app keeps the permissions it was granted until someone reviews and revokes them. It stays in place when the employee who approved it leaves, MFA doesn’t stand in front of it, and it keeps working long after anyone remembers why it was granted.
That isn’t a reason to stop using cloud tools. Modern businesses run on them, and a reputable backup service is still a smart investment. It’s a reason to treat connected apps the way you’d treat a vendor with a physical key to your office: know who has one, know which doors it opens, and take it back when the relationship ends.
Four questions about Microsoft 365 third-party app access
1. Which apps are connected to our Microsoft 365, and what can each one do? Your IT team or provider can pull this list quickly. Ask them to flag anything with broad access, such as permission to read all mail or manage user accounts, and anything nobody can explain.
2. Which of those do we actually still use? The administrator above was exposed through an app they’d stopped using years ago. An unused connection carries all of the risk and none of the benefit. Remove it.
3. Would we know if an app suddenly gave itself admin rights? Microsoft 365 can alert you when someone or something gains administrator rights, when new credentials are added to an app, and when an app signs in from somewhere unusual. Many small and midsize businesses have these alerts available but turned off, or routed to an inbox nobody reads. Ask who receives them and what happens next.
4. If our backup vendor went offline tomorrow, what would we do? Customers of the affected service found their backups simply stopped. Their stored data was reported safe, but “safe and unreachable” isn’t much comfort in the middle of an emergency. Know where your backups live, how long a restore really takes, and whether you have a second copy that doesn’t depend on one vendor’s connection.
If you work with an IT provider, these are fair questions to ask directly. A good partner should answer them plainly and should already be checking your environment in light of this news.
The bigger lesson
We wrote recently about the gap between feeling secure and being secure. This incident fits that pattern exactly. A business could have MFA on every account, strong passwords, and regular phishing training, and still have been exposed, because the weak point was a trusted connection set up long ago and never revisited.
It also explains why insurers keep asking harder questions. If you’ve filled out a cyber insurance application recently, you’ve likely answered questions about vendor access and backups. Incidents like this are the reason those questions exist.
The fix isn’t exotic. It’s an inventory, a cleanup, a few well-routed alerts, and a backup plan that doesn’t rest on a single vendor. None of it requires buying new tools. It just requires someone to look.
Where to start
Share this article with whoever manages your Microsoft 365, and walk through the four questions together. For the technical side, Huntress’s incident write-up is a solid reference for your IT team.
If you’d like a second set of eyes, Altivus can review the apps connected to your Microsoft 365, help you remove what you don’t need, and make sure the right alerts reach a real person.